
Assets | PRA Cloud
Formerly known as Jump Items
What are Assets?
Assets are individual systems or devices that are made available for remote access within an Asset Group, enabling administrators to organize and control access to remote systems in a secure manner.
How are Assets useful to my organization?
Assets allow users to securely access and troubleshoot remote systems, ensuring efficient issue resolution while maintaining control over which systems can be accessed and when. Create Assets to start standard access sessions, web Assets, VNC sessions, and Remote Desktop Protocol sessions, or to shell to SSH-enabled or Telnet-enabled network devices.
You can add and manage Assets from both the Assets page in /login and the Access Console.
How do I access the Assets page?
- Use a Chromium-based browser to sign in to your Privileged Remote Access URL.
This URL is provided in the BeyondTrust welcome email and includes your site URL followed by /login. - From the left menu, click Asset Management.
The Assets page opens and displays by default.
The Assets page
The Assets page lists the Assets that have been created or deployed on your site, and is where you add, edit, copy, and delete them.
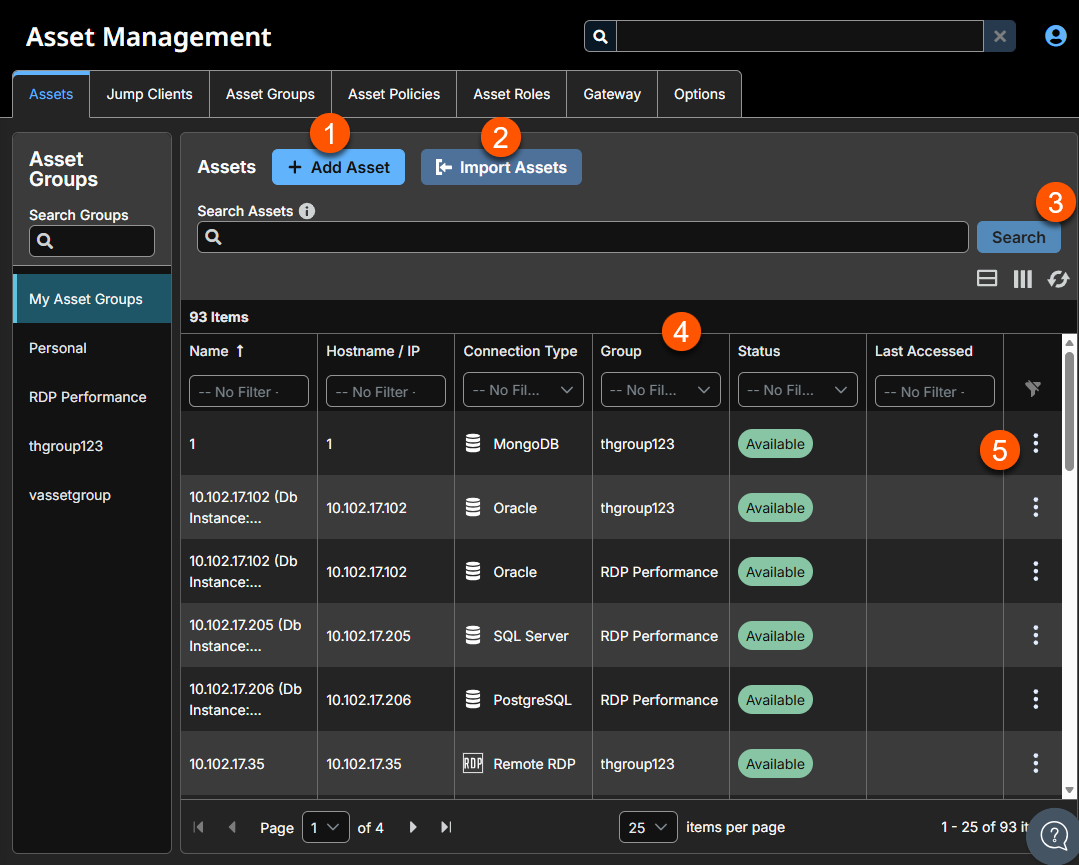
- Add: Add an Asset.
- Import Assets: Use the Assets Mass Import Wizard to bulk import Assets.
- Search: Search for a specific Asset.
- Assets grid: Locate an Asset, then click on it to view its details.
- Actions: Click to Edit, Copy, or Delete an Asset.
Add an Asset
-
On the Assets page, click Add Asset.
-
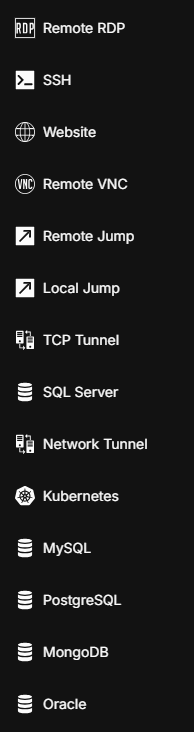
Select the type of Asset you want to add.
-
Complete the fields on the Create New Type Asset. Fields change based on the Asset type selected.
-
Click Save.
- The Asset types you can add depend on your permissions, in the same way they do in the access console. Because the Assets page is not limited to the Asset types the Access console supports, you may see types here that are not available to you there, including TCP tunnels, network tunnels, Kubernetes clusters, and database connections.
- If an Asset type you expect is not listed, check your Asset Role. Asset Roles are set on
the Asset Management > Asset Roles page or the Users & Security > Group Policies
page. For more information, see Asset Roles.
View, edit, copy, or delete an Asset
Click an Asset in the list to see its details. From there you can:
- Edit the Asset's settings.
- Copy the Asset to create a new Asset with the same settings.
- Delete the Asset.
The actions you see depends on your permissions.
Important informationYou cannot start a session from the Assets page. Use the access console or the Privileged Web Access console to connect to an Asset.
Assets found through endpoint search are not listed on this page, because no action can be taken on them here.
Import Assets
You can use the Assets Mass Import Wizard to create Assets for anyone of the following sessions:
- Local Jump
- Remote Jump
- Remote VNC
- Remote RDP
- SSH
- Database Connection
- Web Jump
Important informationLinux Gateways can be used for RDP, SSH/Telnet, Website, Database Connectioning, and VNC sessions. Linux Gateways do allow for credential injection from user or Vault, as well as RemoteApp functionality and Shell filtering. Clustered Gateways can only add new nodes of the same operating system.
You cannot mix Windows and Linux nodes.
When you create a large number of Assets, it may be easier to import them via a spreadsheet than to add them one by one in the representative console.
Import Assets
- On the Assets page, click Import Assets.
- From the dropdown, select the type of Asset you want to import.
- Click Download Template.
A comma-separated values file (*.csv) downloads. - Using the text in the template as your column headers, add a row for each Asset you want to import. You can complete or leave blank any field that is not required. The fields for each Asset type are described in Asset Help.
- Click Next.
- Select your completed CSV file.
- Click Import.
The maximum file size you can upload at one time is 5 MB. Each CSV file can contain only one type of Asset.
Asset Help
Local Asset help
| Parameter | API Value | Required | Default Value | Description |
|---|---|---|---|---|
| Hostname | local_jump_hostname | Yes | The hostname of the endpoint to be accessed by this Asset. This string has a maximum of 128 characters. | |
| Name | name | Yes | The name of the endpoint to be accessed by this Asset. This string has a maximum of 128 characters. | |
| Asset Group | group | Yes | The code name of the Asset Group with which this Asset should be associated. | |
| Tag | tag | No | You can organize your Assets into categories by adding a tag. This string has a maximum of 64 characters. | |
| Comments | comments | No | You can add comments to your Assets. This string has a maximum of 1024 characters. | |
| Asset Policy | jump_policy | No | The code name of an Asset Policy. You can specify an Asset Policy to manage access to this Asset. | |
| Session Policy | session_policy | No | The code name of a Session Policy. You can specify a Session Policy to manage the permissions available on this Asset. | |
| Endpoint Agreement Policy | endpoint_agreement_policy | No | no_prompt | The value "accept" will automatically accept the endpoint agreement if it times out and allow the session to start. The value "reject" will automatically reject the endpoint agreement and stop the session from starting. The value "no_prompt" will not show an endpoint agreement even if the feature is configured. This field has no effect if the global endpoint agreement setting is not enabled. |
Remote Asset help
| Parameter | API Value | Required | Default Value | Description |
|---|---|---|---|---|
| Hostname | remote_jump_hostname | Yes | The hostname of the endpoint to be accessed by this Asset. This string has a maximum of 128 characters. | |
| Gateway | jumpoint | Yes | The code name of the Gateway through which the endpoint is accessed. | |
| Name | name | Yes | The name of the endpoint to be accessed by this Asset. This string has a maximum of 128 characters. | |
| Asset Group | group | Yes | The code name of the Asset Group with which this Asset should be associated. | |
| Tag | tag | No | You can organize your Assets into categories by adding a tag. This string has a maximum of 64 characters. | |
| Comments | comments | No | You can add comments to your Assets. This string has a maximum of 1024 characters. | |
| Asset Policy | jump_policy | No | The code name of an Asset Policy. You can specify an Asset Policy to manage access to this Asset. | |
| Session Policy | session_policy | No | The code name of a Session Policy. You can specify a Session Policy to manage the permissions available on this Asset. | |
| Endpoint Agreement Policy | endpoint_agreement_policy | No | no_prompt | The value "accept" will automatically accept the endpoint agreement if it times out and allow the session to start. The value "reject" will automatically reject the endpoint agreement and stop the session from starting. The value "no_prompt" will not show an endpoint agreement even if the feature is configured. This field has no effect if the global endpoint agreement setting is not enabled. |
Remote VNC Asset help
| Parameter | API Value | Required | Default Value | Description |
|---|---|---|---|---|
| Hostname | remote_vnc_hostname | Yes | The hostname of the endpoint to be accessed by this Asset. This string has a maximum of 128 characters. | |
| Gateway | jumpoint | Yes | The code name of the Gateway through which the endpoint is accessed. | |
| Port | port | No | 5900 | A valid port number from 100 to 65535. |
| Name | name | Yes | The name of the endpoint to be accessed by this Asset. This string has a maximum of 128 characters. | |
| Asset Group | group | Yes | The code name of the Asset Group with which this Asset should be associated. | |
| Tag | tag | No | You can organize your Assets into categories by adding a tag. This string has a maximum of 64 characters. | |
| Comments | comments | No | You can add comments to your Assets. This string has a maximum of 1024 characters. | |
| Asset Policy | jump_policy | No | The code name of an Asset Policy. You can specify an Asset Policy to manage access to this Asset. | |
| Session Policy | session_policy | No | The code name of a Session Policy. You can specify a Session Policy to manage the permissions available on this Asset. |
Remote RDP Asset help
| Parameter | API Value | Required | Default Value | Description |
|---|---|---|---|---|
| Hostname | remote_rdp_hostname | Yes | The hostname of the endpoint to be accessed by this Asset. This string has a maximum of 128 characters. | |
| Gateway | jumpoint | Yes | The code name of the Gateway through which the endpoint is accessed. | |
| Username | rdp_username | No | The username to sign in as. | |
| Domain | domain | No | The domain the endpoint is on. | |
| Quality | quality | No | best_performance | The quality at which to view the remote system. Can be black_white (Black & White for lowest bandwidth consumption), few_colors (8-bit color quality), more_colors (16-bit color for medium color quality performance), full_colors (32-bit for true color reproduction), best_performance (VP9 codec for more fluid video), or lossless (high definition for exact reproduction). This cannot be changed during the Remote Desktop Protocol (RDP) Session. |
| Console Session | console | No | 0 | 1: Starts a console session. 0: Starts a new session. |
| Ignore Untrusted Certificate | ignore_untrusted | No | 0 | 1: Ignores certificate warnings. 0: Shows a warning if the server's certificate cannot be verified. |
| SecureApp Type | secure_app_type | No | none | The SecureApp launch method. Can be "none", "remote_app" (to use RDP's built-in RemoteApp functionality), "remote_desktop_agent" (to use BeyondTrust's Remote Desktop Agent), or "remote_desktop_agent_credentials" (to use BeyondTrust's Remote Desktop Agent with Credential Injection). If "remote_desktop_agent" or "remote_desktop_agent_credentials" are chosen then the Remote Desktop Agent must be installed on the remote system. |
| RemoteApp Name | remote_app_name | No | The RemoteApp program name. This string has a maximum of 520 characters. | |
| RemoteApp Parameters | remote_app_params | No | A space-separated list of parameters to pass to the RemoteApp. Parameters with spaces can be quoted using double-quotes. This string has a maximum of 16000 characters. | |
| Remote Executable Path | remote_exe_path | No | The path to the remote executable that will be launched using the Remote Desktop Agent. This can only be used if the SecureApp Type uses the Remote Desktop Agent. | |
| Remote Executable Parameters | remote_exe_params | No | A space-separated list of parameters to pass to the remote executable that will be launched using the Remote Desktop Agent. Parameters with spaces can be quoted using double-quotes. This can only be used if the SecureApp Type uses the Remote Desktop Agent. | |
| Target System | target_system | No | The name of the target system being accessed by the remote application. This value is used to limit the list of injected credentials to only those that are valid on the target system. This value can only be used if the SecureApp Type uses the Remote Desktop Agent with Credential injection. | |
| Credential Type | credential_type | No | The type of credentials that will be injected into the remote executable. This value will depend on the password vault from which credentials are retrieved. This value can only be used if the SecureApp Type uses the Remote Desktop Agent with Credential injection. | |
| Name | name | Yes | The name of the endpoint to be accessed by this Asset. This string has a maximum of 128 characters. | |
| Asset Group | group | Yes | The code name of the Asset Group with which this Asset should be associated. | |
| Tag | tag | No | You can organize your Assets into categories by adding a tag. This string has a maximum of 64 characters. | |
| Comments | comments | No | You can add comments to your Assets. This string has a maximum of 1024 characters. | |
| Asset Policy | jump_policy | No | The code name of an Asset Policy. You can specify an Asset Policy to manage access to this Asset. | |
| Session Forensics | session_forensics | No | 0 | 1: Enables RDP with Session Forensics functionality. 0: Uses normal RDP functionality. |
| Session Policy | session_policy | No | The code name of a Session Policy. You can specify a Session Policy to manage the permissions available on this Asset. |
Shell Asset help
| Parameter | API Value | Required | Default Value | Description |
|---|---|---|---|---|
| Hostname | shelljump_hostname | Yes | The hostname of the endpoint to be accessed by this Asset. This string has a maximum of 128 characters. | |
| Gateway | jumpoint | Yes | The code name of the Gateway through which the endpoint is accessed. | |
| Username | shelljump_username | No | The username to sign in as. | |
| Protocol | protocol | Yes | Can either be "ssh" or "telnet". | |
| Port | port | No | SSH: 22, Telnet: 23 | A valid port number from 1 to 65535. Defaults to 22 if the protocol is SSH or 23 if the protocol is Telnet. |
| Terminal Type | terminal | No | xterm | Can be either xterm or vt100. |
| Keep-Alive | keep_alive | No | The number of seconds between each packet sent to keep an idle session from ending. Can be any number from 5 to 300 or blank to disable the feature. | |
| Name | name | Yes | The name of the endpoint to be accessed by this Asset. This string has a maximum of 128 characters. | |
| Asset Group | group | Yes | The code name of the Asset Group with which this Asset should be associated. | |
| Tag | tag | No | You can organize your Assets into categories by adding a tag. This string has a maximum of 64 characters. | |
| Comments | comments | No | You can add comments to your Assets. This string has a maximum of 1024 characters. | |
| Asset Policy | jump_policy | No | The code name of an Asset Policy. You can specify an Asset Policy to manage access to this Asset. | |
| Session Policy | session_policy | No | The code name of a Session Policy. You can specify a Session Policy to manage the permissions available on this Asset. |
Database Connection help
| Parameter | API Value | Required | Default Value | Description |
|---|---|---|---|---|
| Hostname | protocol_tunnel_hostname | Yes | The hostname of the endpoint to be accessed by this Asset. This string has a maximum of 128 characters. | |
| Gateway | jumpoint | Yes | The code name of the Gateway through which the endpoint is accessed. | |
| Name | name | Yes | The name of the endpoint to be accessed by this Asset. This string has a maximum of 128 characters. | |
| Asset Group | group | Yes | The code name of the Asset Group with which this Asset should be associated. | |
| Tunnel Type | tunnel_type | No | tcp | The type of tunnel which is one of IP, K8S, MSSQL, MySQL, PSQL, or TCP. |
| Tunnels | tcp_tunnels | No | The list of one or more tunnel definitions. It is required when the tunnel type is TCP. A tunnel definition is a mapping of a TCP port on the local user's system to a TCP port on the remote system specified by the hostname. Any connection made to the local port will cause a connection to be made to the remote port, allowing data to be tunnelled between local and remote systems. Multiple mappings should be separated by a semicolon. An example input for this field is "auto->22;3306->3306". In this example, a randomly chosen local port maps to remote port 22, and local port 3306 maps to remote port 3306. | |
| Filter Rules | filter_rules | No | The list of one or more filter rules. It is required when the tunnel type is IP. A filter rule is required to contain an IP address rule, and may contain an optional port rule and optional IANA protocol keyword (default ANY), each separated by a space in the order of: IP rule, port rule, protocol number. Multiple rules should be separated by a semicolon. An IP rule is either a range in the form of two IPv4 addresses separated by a dash, a list in the form of 1 or more IPv4 addresses separated by a comma, or CIDR notation IP address. A port rule is either a range of port numbers (from 1 to 65535) in the form of two ports separated by a dash or a list in the form of 1 or more ports separated by a comma. An example input for this field is "192.168.12.0/24 9000 TCP;192.168.1.10-192.168.1.20 8000-8005 UDP;192.168.2.10,192.168.2.20 ANY;10.10.10.10 ICMP;127.0.0.1 90,9000 TCP". | |
| Username | username | No | The username which is required when the tunnel type is mssql. This string has a maximum of 128 characters. | |
| Database | database | No | The database which is used when the tunnel type is mssql. This string has a maximum of 128 characters. | |
| Local Address | local_address | No | 127.0.0.1 | The local address on which the system will be listening for connections to the defined tunnels. The value must be within the 127.0.0.0/24 subnet. |
| Tag | tag | No | You can organize your Assets into categories by adding a tag. This string has a maximum of 64 characters. | |
| Comments | comments | No | You can add comments to your Assets. This string has a maximum of 1024 characters. | |
| Asset Policy | jump_policy | No | The code name of an Asset Policy. You can specify an Asset Policy to manage access to this Asset. | |
| Session Policy | session_policy | No | The code name of a Session Policy. You can specify a Session Policy to manage the permissions available on this Asset. | |
| URL | url | No | The url which is used for Kubernetes tunnel Assets. This string has a maximum of 256 characters. | |
| CA Certificates | ca_certificates | No | The certificate which is used for Kubernetes tunnel Assets. This string has a maximum of 12288 characters. |
Web Asset Help
| Parameter | API Value | Required | Default Value | Description |
|---|---|---|---|---|
| Name | website_name | Yes | The name of the Website to be accessed by this Asset. | |
| Gateway | jumpoint | Yes | The code name of the Gateway through which the endpoint is accessed. | |
| Asset Group | group | Yes | The code name of the Asset Group with which this Asset should be associated. | |
| Tag | tag | No | You can organize your Assets into categories by adding a tag. This string has a maximum of 64 characters. | |
| Comments | comments | No | You can add comments to your Assets. This string has a maximum of 1024 characters. | |
| Asset Policy | jump_policy | No | The code name of an Asset Policy. You can specify an Asset Policy to manage access to this Asset. | |
| Session Policy | session_policy | No | The code name of a Session Policy. You can specify a Session Policy to manage the permissions available on this Asset. | |
| URL | url | Yes | The website's URL. The URL must begin with a protocol of either "http" or "https". | |
| Verify Certificate | verify_certificate | No | 1 | 1: Verify certificate validity and, if there are problems, prevent the session from starting. 0: Ignore all certificate problems. |
| Username Format | username_format | No | passthru | passthru: Pass the username through directly from the credential provider. username_only: If the username is in UPN (Username@Domain) or DLLN (DOMAIN\Username) format then the domain is removed. Only the username is injected. |
| Username Field Hint | username_field_hint | No | A CSS style query selector that identifies the username field to help with the initial credential injection. If this value is provided and a matching element is not found, then the credential injection will fail. | |
| Password Field Hint | password_field_hint | No | A CSS style query selector that identifies the password field to help with the initial credential injection. If this value is provided and a matching element is not found, then the credential injection will fail. | |
| Submit Button Hint | submit_button_hint | No | A CSS style query selector that identifies the submit button to help with the initial credential injection. If this value is provided and a matching element is not found, then the credential injection will fail. | |
| Auth Timeout | authentication_timeout | No | 3 | The amount of time in seconds the web Jump Client should wait for authentication to succeed before timing out. This can be any number from 1 to 30. |
Web Jump client certificates for Microsoft Entra conditional access
What this release does
Web Jump now answers a client certificate request. An administrator picks one certificate that already lives on a Windows Jumpoint. When a website, or the identity provider behind it, asks for a certificate, Web Jump presents that certificate automatically.
This lets technicians reach sites whose Entra policy accepts certificate-based authentication. Customers no longer need an IP exception or a fallback to RDP.
What this release does not do
This release does not provide the following:
- Web Jump does not present device identity, so compliant-device / hybrid-join CA evaluation remain unsupported.
- Web Jump does not prove that a device is compliant or hybrid joined.
- Web Jump does not use the Windows sign in broker (WAM) or device tokens (PRT).
You manage all certificate-based authentication requirements, including installing the certificate on the computer, providing access to its private key, and configuring the Microsoft Entra policy that trusts the certificate.
How it works
Each Jumpoint uses one certificate for every Web Jump session that runs through it. The administrator names that certificate in the Windows registry:
- Key:
HKLM\SOFTWARE\BeyondTrust - Value:
WebJumpClientCertificateThumbprint - Type:
REG_SZ - Data: the certificate's SHA-1 thumbprint
The thumbprint is the 40-character code that Windows shows for each certificate. Web Jump ignores spaces, colons, dashes, and letter case. If the value is not 40 hex characters after cleanup, Web Jump treats it as malformed and logs a warning.
Web Jump reads this value each time a session starts. You do not need to restart the Jumpoint service.
Where the certificate must live
The Web Jump browser runs as the Windows SYSTEM account. It only looks in that account's Personal certificate store. It never looks in the computer's main store (LocalMachine\My). It also never looks in your own store, which is where a certificate goes when you double-click a PFX file.
To install the certificate in the correct place:
- Open
mmcand add the Certificates snap-in. - Select Service account, then Local computer.
- Select the
sra-jumpoint-<host>service. - Open Personal and import the certificate. Include the private key.
What users see
| Situation | What happens | Jumpoint log | Rep sees |
|---|---|---|---|
| The site never asks for a certificate | Nothing changes. | No entry | Nothing |
| The site asks, and no certificate is named | The session continues without a certificate. | client certificate requested by <host>; none designated | Nothing |
| The site asks, and the named certificate is installed | Web Jump presents the certificate. | presenting designated client certificate <thumbprint> to <host> | Nothing |
| The site asks, but the certificate is missing, its key is unreadable, or the value is malformed | The session continues without a certificate. | designated client certificate <thumbprint> is not available on this Jumpoint (requested by <host>) | "The Jumpoint's designated certificate could not be presented." |
Known limitation
When a site asks for a certificate, it lists the certificate authorities (CAs) it trusts. The browser hides any certificate from a CA that is not on that list. In this case, a valid, installed certificate still looks not available.
To validate, run the following syntax from a workstation:
curl --cert <cert> --key <key> https://<site>/Use Web Jump with multi-step SSO login pages
Many websites use single sign-on (SSO) to sign users in. Some SSO sign in flows ask for your username on more than one page before they ask for your password. Web Jump now handles these flows. PRA injects the credential on every page of the sign in sequence, so users reach the target website without typing anything.
What changed
Before version 26.3, Web Jump credential injection supports a standard two-page sign in: one page for the username and one page for the password. If a website asks for the username a second time, injection stops. The user must type the username by hand, and PRA does not inject the password on the next page.
In version 26.3, Web Jump recognizes each page that asks for an identifier. PRA injects the username on each of these pages and then injects the password on the final page.
| How users sign in | Before 26.3 | 26.3 and later |
|---|---|---|
| Username, then password | Supported | Supported |
| Username, username, then password | Stops on the second username page | Supported |
How it works
A common example is a service provider–initiated SSO flow that passes the user from one identity provider to another:
- The user starts a Web Jump session to the target website.
- The website sends the user to the first identity provider, such as Microsoft Entra ID. PRA injects the username.
- The first identity provider redirects the user to a second identity provider, such as Ping Identity. This page asks for the username again. PRA injects the username again.
- The second identity provider shows the password page. PRA injects the password.
- The user signs in to the target website.
ImportantPRA uses the same credential for every step. The credential can come from the PRA vault or from Password Safe, including Password Safe managed supplemental administrative accounts.
Benefits
- Users sign in without manual steps. PRA completes the full sign in flow, even when it spans several pages and identity providers.
- Credentials stay protected. Users never see or type the password, and PRA keeps the session governed and recorded.
- Your SSO setup stays the same. You do not need to change the website's sign in entry point or the SSO experience for other users.
- PRA and Password Safe work together. You can inject Password Safe managed credentials into web sessions instead of building a separate Password Safe application session for the website.
Before you begin
Make sure you have:
- PRA version 26.3 or later.
- A Web Jump Item for the target website.
- A credential for the website stored in the PRA vault or in Password Safe.
- Permission to use that credential with the Web Jump Item.
Set up a Web Jump Item for a multi-step SSO website
- In the Web console, create or edit the Web Jump Item for the target website.
- In URL, enter the address of the target website. Use the website's normal entry point. Do not point directly to an identity provider page.
- Set up credential injection for the item as you do for any Web Jump Item.
- Associate the credential with the item. If you use Password Safe, select the Password Safe managed account.
- Save the Web Jump Item.
ImportantPRA detects the extra username pages automatically. You do not need to list or map each page.
Test the user sign in
- Start a session from the Web Jump Item.
- Watch each sign in page. PRA fills in the username on each username page and the password on the last page.
- Confirm that the target website opens and that you are signed in.
Troubleshoot
| Problem | What to check |
|---|---|
| PRA stops on a page and does not fill in the username | Make sure you run PRA 26.3 or later. Check whether the page shows a CAPTCHA, which PRA cannot complete. |
| PRA fills in the username but not the password | Confirm the credential is correct and not expired. Check that the Password Safe account is available to the user. |
| The sign in page shows an error for the username format | Check whether the identity provider expects a format such as [email protected] or DOMAIN\user, and update the stored credential to match. |
| The flow asks for something other than a username or password, such as a one-time code | The user must complete that step by hand. This feature covers repeated username pages and the password page only. |
Limitations
This feature focuses on sign in pages that ask for a username one or more times and then a password. It does not do the following:
- Run custom browser scripts.
- Follow sign in flows that branch based on conditions.
- Fill in web forms that are not part of the sign in process.
- Complete CAPTCHA challenges.
Updated 24 days ago
